Research · InfosecFeed Brief
Russian State-Sponsored Hackers Use Claude to Rebuild Malware After Detection
What you need to know
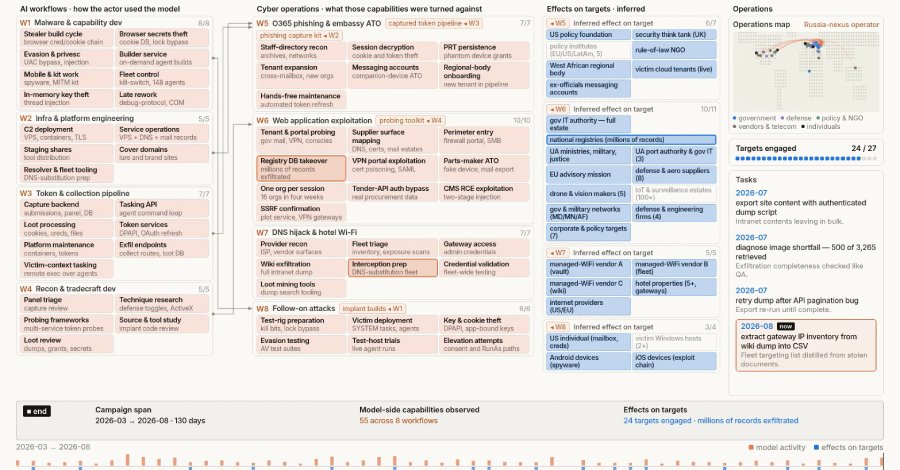
Anthropic on Thursday revealed it disrupted a campaign mounted by a Russian state-sponsored threat actor that abused Claude for developing an AI-assisted workflow to get ahead of the detection curve. The operation has been attributed to a cyber espionage group it calls GTG-20006 (where "GTG" stands for Generative Threat Group), which aligns with broader…
Source transparency
Read the original report at The Hacker News ↗
This is an InfosecFeed curated brief based on reporting from The Hacker News. InfosecFeed does not claim ownership of the original reporting.