Vulnerabilities · InfosecFeed Brief
New WordPress Click2Shell Flaw Forces Theme Installs, Can Chain to Code Execution
What you need to know
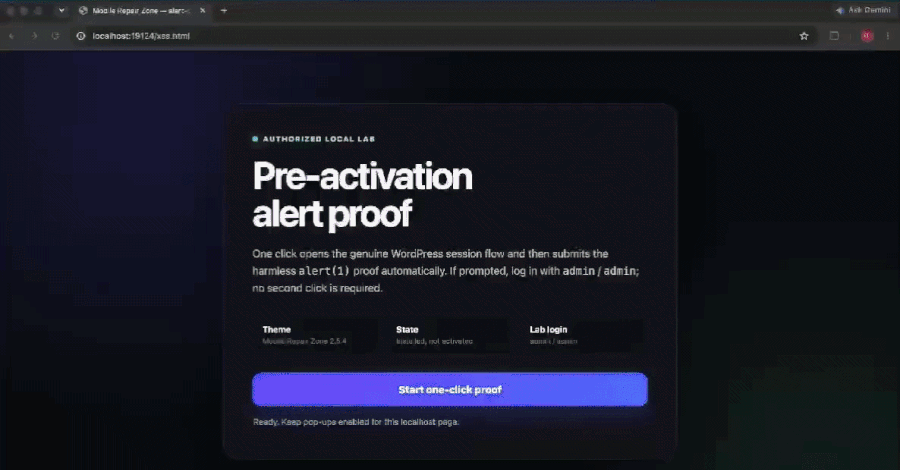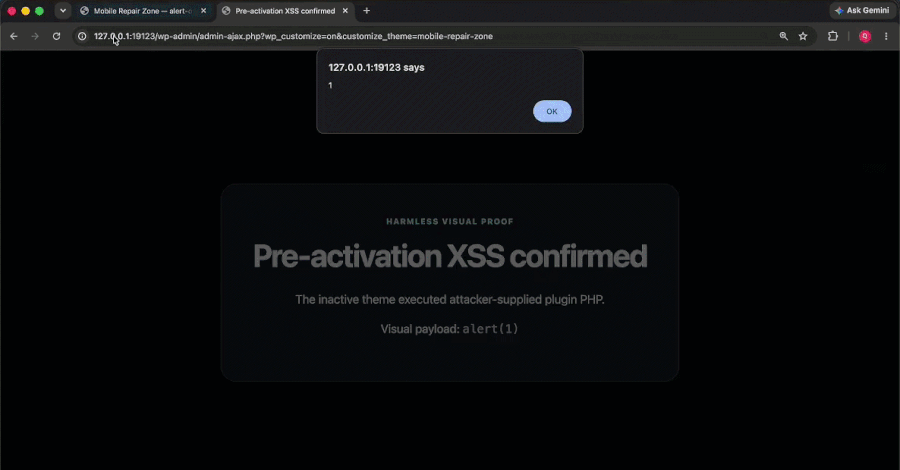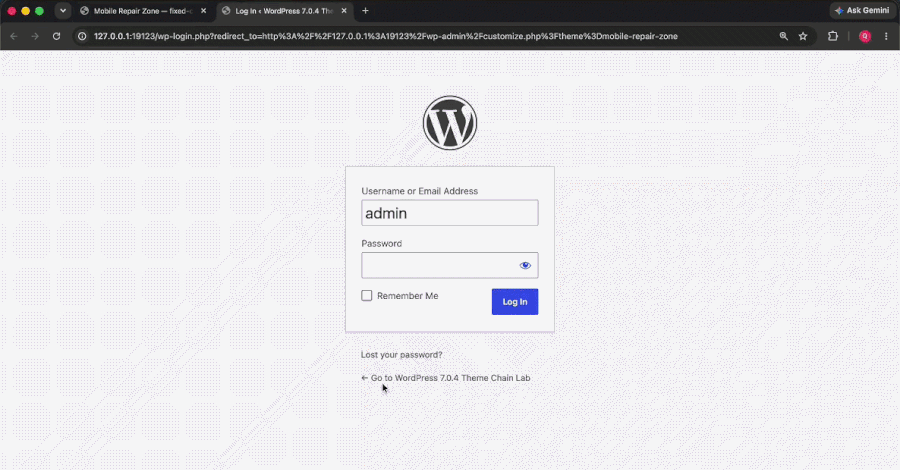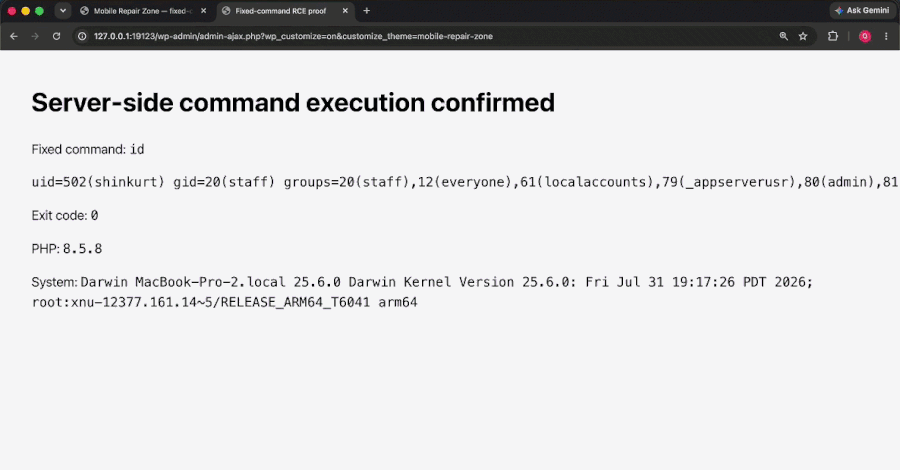
WordPress today released patches to fix a new set of vulnerabilities in its core software, one of which could allow a crafted web link, opened by a logged-in administrator, to install a theme from the official WordPress.org directory without anyone clicking Install. The security firm pwn.ai, whose researchers reported the flaw, calls the attack chain…
Source transparency
Read the original report at The Hacker News ↗
This is an InfosecFeed curated brief based on reporting from The Hacker News. InfosecFeed does not claim ownership of the original reporting.