Vulnerabilities · InfosecFeed Brief
Exploit Released for Unpatched Ubuntu Linux Flaw Enabling Host-Root Container Escape
What you need to know
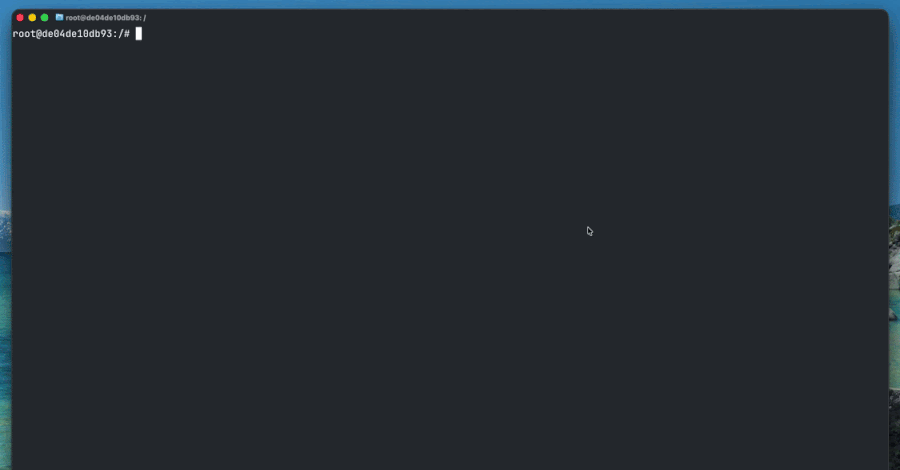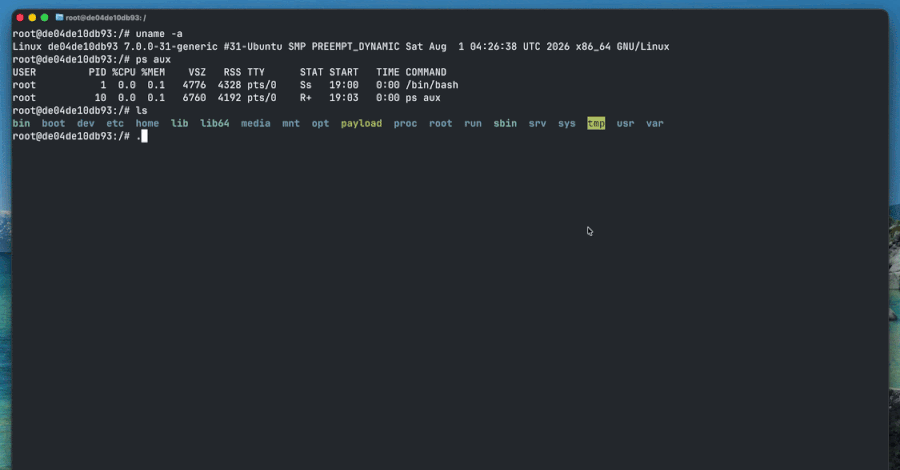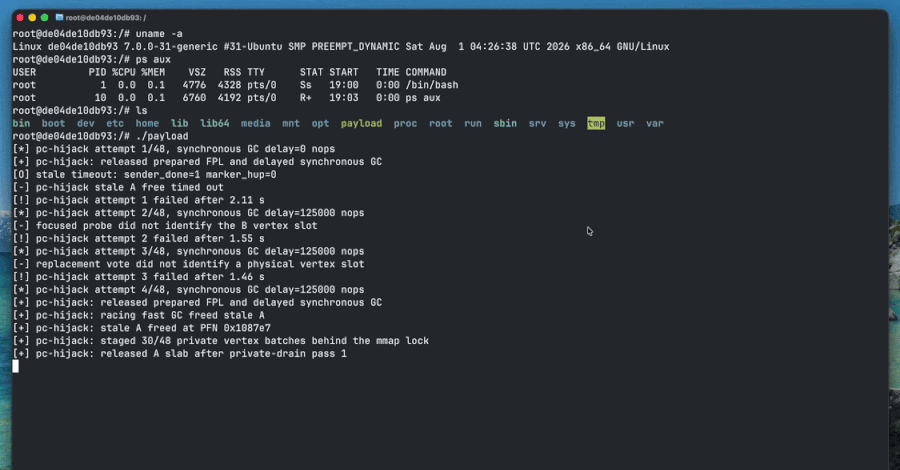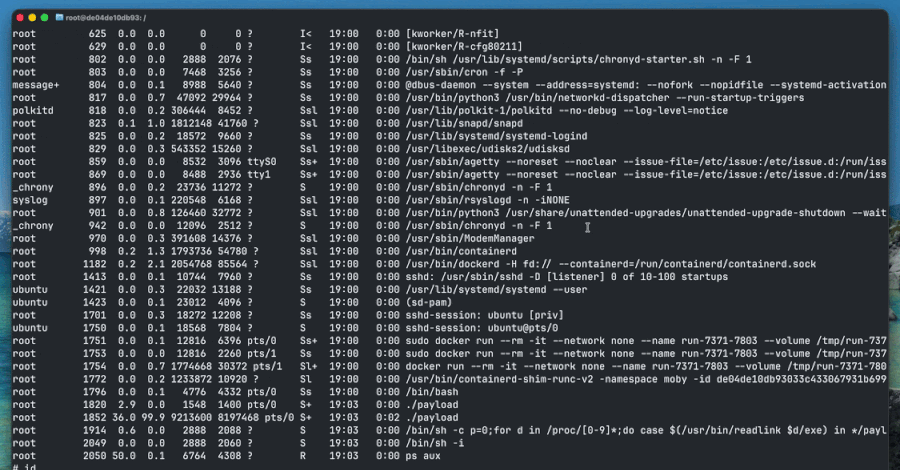
A use-after-free in the Linux kernel's AF_UNIX socket subsystem can be used to escape a container and gain root on the host, security firm DepthFirst said in research published September 22. The flaw, tracked as CVE-2026-80521 (CVSS score: 7.8), was fixed upstream on August 6, but Ubuntu has not shipped the patch for its 26.04, 24.04, or 22.04 LTS…
Source transparency
Read the original report at The Hacker News ↗
This is an InfosecFeed curated brief based on reporting from The Hacker News. InfosecFeed does not claim ownership of the original reporting.