Vulnerabilities · InfosecFeed Brief
Critical FortiMail Zero-Day Flaw Exploited in Attacks Allows Unauthenticated Arbitrary File Writes
What you need to know
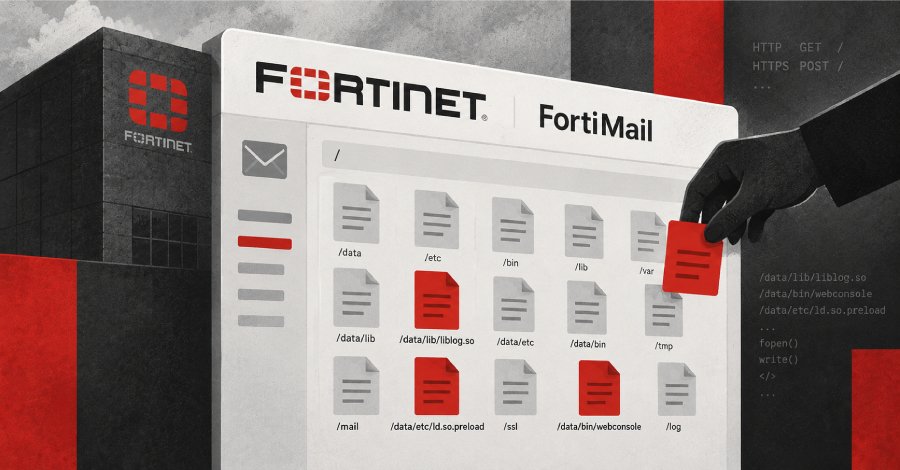
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), on Thursday, added a critical security flaw impacting Fortinet FortiMail to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation. The vulnerability, tracked as CVE-2026-104286 (CVSS score: 9.8), allows unauthenticated attackers to write arbitrary files…
Source transparency
Read the original report at The Hacker News ↗
This is an InfosecFeed curated brief based on reporting from The Hacker News. InfosecFeed does not claim ownership of the original reporting.